3-2-1 Backup Rule: What the Classic Formula Misses About Ransomware Survival
October 29, 2026
Adding an offline or immutable backup and confirming zero errors through recovery testing are what separate a backup plan that survives ransomware from one that only handles hardware failure. The 3-2-1-1-0 approach closes gaps the original rule leaves open.
Most businesses assume the 3-2-1 backup rule is a finished checklist, but in practice it only covers part of the threat picture. Following it to the letter can still leave a company unable to recover from a targeted attack.
The gap shows up most clearly when the failure isn't a broken drive but a deliberate one. A backup strategy is only as strong as its weakest link, and one overlooked flaw can expose a business to threats like ransomware, not just hardware breakdowns. Since the consequences of that exposure are immediate, the stakes are worth spelling out before going further: losing access to company data can mean halted operations, lost revenue, and lasting damage to reputation, and when a backup plan fails, those costs land at once.
The 3-2-1 backup rule earned its reputation for a reason. It calls for three copies of your data, stored on two different types of media, with one copy kept off-site, and that structure covers a wide range of everyday risks. What it doesn't account for is the era it was designed in, well before ransomware became a daily threat.
That timing gap matters because today's attackers don't stop at production data; they go after backups too. Protecting a business now means going beyond the classic checklist and addressing the risks modern threats actually pose.
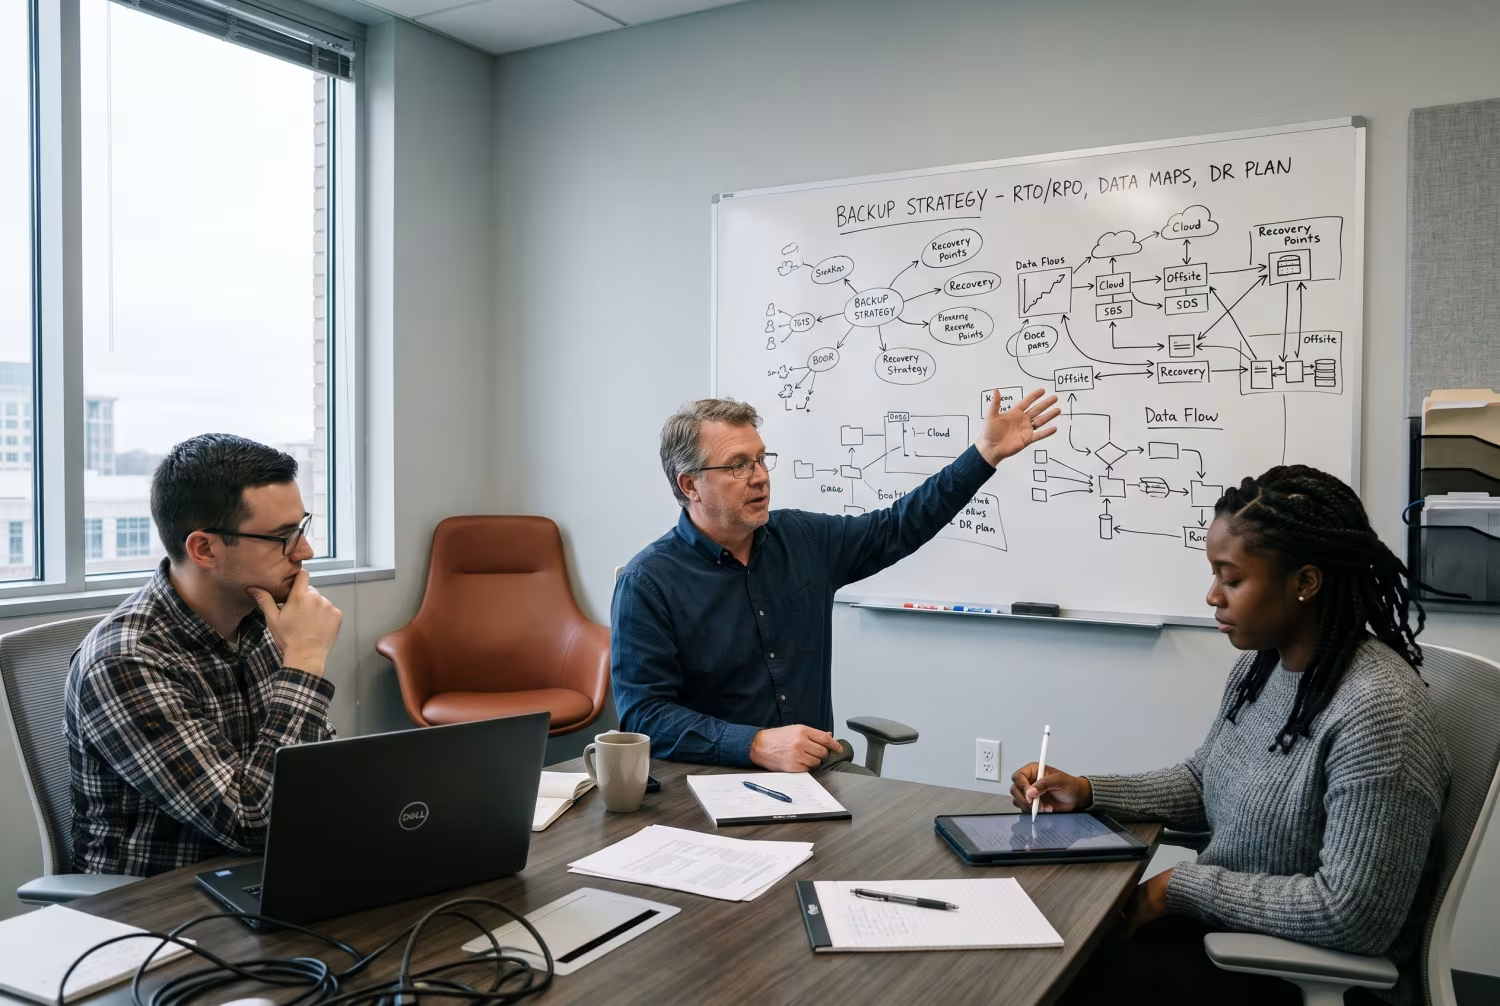
Why the classic 3-2-1 backup rule falls short
Many businesses in Charlotte lean on the 3-2-1 backup rule, trusting that it covers all their data loss risks. It's a strong foundation, but it wasn't built with today's ransomware tactics in mind.
Ransomware complicates that foundation because it can encrypt not just main files but any connected backups too. If backup copies stay online or remain easily changed, they can be locked or deleted right alongside the original data, which means following the classic rule to the letter can still leave a business unable to recover after an attack.
There's a second gap beneath the first: the original rule assumes that simply having copies is enough. Without regular testing, though, those copies might be incomplete or corrupted, and there's often no way to know until recovery is already too late. A plan that looks solid on paper can still fail in practice if nobody checks it.
Taken together, these gaps point to the same conclusion: modern threats demand more than multiple copies. They call for backup strategies built to survive deliberate attacks and prove their own reliability before disaster strikes.
What the 3-2-1-1-0 backup approach adds
The 3-2-1-1-0 backup method takes the classic rule as its base and adds two further requirements, each aimed at closing a gap that ransomware and other advanced threats routinely exploit.
The first addition calls for at least one backup copy kept offline or made immutable. An offline backup sits disconnected from the network, out of malware's reach, while an immutable backup is locked so it can't be changed or deleted for a set period. Either way, attackers who get into a system still can't easily destroy every copy of the data.
The second addition is zero errors, confirmed through recovery testing. Rather than trusting that backups work, this means proving it by restoring data on a regular schedule and fixing any errors before they turn into a real problem.
Together, these two additions mark the line between a backup plan that survives a hardware failure and one that can also withstand a targeted ransomware attack.
The 3-2-1 backup rule in practice: What businesses need to check
A backup plan can look complete on paper and still fail at the exact moment it's needed, which is why testing it against real-world threats matters more than admiring it on a spec sheet. Here's how the 3-2-1-1-0 approach reshapes what to look for.
Offline or immutable backup: Not just off-site
Storing a backup off-site helps, but if that copy stays connected to the network, ransomware can still reach it. An offline backup, such as a tape or drive kept physically separate, can't be attacked remotely, while an immutable backup, often available through modern backup software or select cloud storage providers, locks the data against changes or deletion for a set time.
Recovery testing: More than just backup logs
Backup software might report that jobs completed successfully, but that status alone doesn't guarantee the data can actually be restored. Testing restoration of files or entire systems on a regular basis is the only way to confirm backups are usable and error-free.
Media types: Avoiding a single point of failure
Using two different types of media, such as disk and cloud storage, protects against the failure of any one method. When every backup lives on the same type of device, a single flaw or attack can wipe them all out at once.
Off-site location: Physical separation matters
Keeping one backup copy off-site guards against disasters like fire or flooding, but off-site alone doesn't guarantee offline or immutable. That off-site backup still needs protection from ransomware and accidental deletion to do its job fully.
Zero errors: Fix issues before they matter
Testing backups means watching for errors or missing files and fixing problems the moment they surface, rather than discovering them in the middle of a real emergency.
How ransomware targets backup strategies
Ransomware attacks have grown more sophisticated, and backup copies are now often part of the target rather than an afterthought. Attackers know that easy data restoration removes any pressure to pay the ransom, so they hunt for connected backups and try to encrypt or delete them.
That targeting is exactly why offline or immutable copies matter: without them, a backup process leaves a business exposed. Cloud backup solutions can help close that gap, but only when they include features like versioning or immutability; cloud storage on its own may do little against a determined attacker.
None of that protection means anything without verification, which is why regular testing remains the only real way to confirm data can be restored after an attack. A backup that's never been tested may already be incomplete or corrupted, leaving nothing to fall back on when it counts.
Key elements of a modern backup strategy
A strong backup plan today has to do more than follow the old rules. These are the elements that make the real difference:
- Multiple copies: Always keep at least three copies of your data, including the original and two backups.
- Different media: Use two different types of storage, such as local disk and cloud, to avoid a single point of failure.
- Off-site storage: Store at least one backup in a different physical location to protect against disasters.
- Offline or immutable copy: Make sure one backup is either disconnected from your network or locked so it can't be changed.
- Regular recovery testing: Restore files or systems on a set schedule to confirm zero errors and full recoverability.
Applying the 3-2-1-1-0 rule in Charlotte
Businesses in Charlotte face the same baseline data loss risks as anywhere else, though local factors like severe weather or regional outages add their own pressure on top. Following the 3-2-1-1-0 rule addresses both layers at once, guarding against hardware failure alongside ransomware, accidental deletion, and disasters capable of taking out a main office entirely.
Cloud backup shows up in many local strategies, and it can be effective, but only when the provider actually supports immutable backups or offline options, since those features aren't universal by default.
Testing ties all of this together: without a recent test of the recovery process, there's no real way to know if backups are safe. Ask yourself: when was the last time you restored data from your backups, and did everything work as expected?
The difference between surviving hardware failure and ransomware
A backup plan built strictly on the classic 3-2-1 rule can bring a business back from a failed hard drive or a server crash. Ransomware plays by different rules, though, reaching into every connected system, including any backup left unprotected by offline or immutable storage.
That's precisely where the 3-2-1-1-0 approach earns its keep: keeping one copy offline or immutable, combined with zero errors confirmed through recovery testing, means backups stay intact even after attackers get into the network, and restoration is a certainty rather than a hope when it matters most.
If a current backup solution doesn't meet these standards, the moment to review and update it is now, since the cost of waiting until after an attack always outweighs the effort of preparing beforehand.
How we help Charlotte businesses close backup gaps
Many companies with 20 to 80 employees find that their backup plans look solid until a real crisis tests them. At Sterling, we understand how easy it is to overlook the details that matter most.
If you’re unsure whether your backups could survive ransomware, let’s talk about how we approach backup testing and offline protection. We’re ready to help you review your setup and make sure your data is truly safe.
Want faster help when backup issues strike?
Get an average response and resolution time of only 30 minutes when you need support—so your backup problems don’t turn into business downtime.
Frequently asked questions
How often should we test our backup recovery process?
Backup recovery should be tested at least once a quarter, or more often if data changes frequently. Regular testing catches errors early and confirms that critical data can actually be restored when needed.
What does an immutable backup mean for our business?
An immutable backup is a copy of data that cannot be changed or deleted for a set period. That protection shields backups from ransomware and accidental deletion, making it far harder for attackers to destroy every copy at once.
Can cloud backup alone protect us from ransomware?
Cloud backup helps only when the provider offers features like immutability or offline storage. Without them, ransomware can still reach cloud backups if credentials are compromised, so it's worth checking a provider's options for extra protection.
What's the risk of using only one type of backup media?
Relying on a single type of storage, such as external hard drives alone, creates a single point of failure. If that media fails or gets targeted by malware, every backup copy could be lost at once.
How do we know if our backup solution is following best practice?
Check the process against the 3-2-1-1-0 rule: three copies, two media types, one off-site, one offline or immutable, and zero errors confirmed by testing. Missing any of these steps means the plan may not be fully protecting the business.
Landon Carter
Outside of work I enjoy traveling with my wife and son, helping coach little league baseball teams, and cheering on the Carolina Panthers.


